GHSA-v4v2-8h88-65qj
Attribute Injection leading to XSS(Cross-Site-Scripting)
Quick fix
GHSA-v4v2-8h88-65qj — uptime-kuma: upgrade to the fixed version with the command below.
npm install uptime-kuma@1.23.7Details
### Summary Google Analytics element Attribute Injection leading to XSS
### Details Since the custom status interface can set an independent Google Analytics ID and the template has not been sanitized, there is an attribute injection vulnerability here, which can lead to XSS attacks. 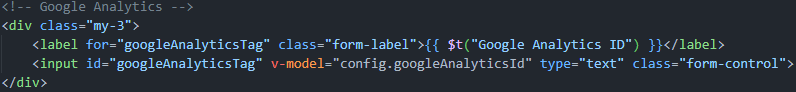
### PoC 1. Run the latest version of the louislam/uptime-kuma container and initialize the account password. 2. Create a new status page. 3. Edit the status page and change the Google Analytics ID to following payload(it only works for firefox. Any attribute can be injected, but this seems the most intuitive): ``` 123123" onafterscriptexecute=alert(window.name+1),eval(window.name) a="x ```
4. Click Save and return to the interface. XSS occurs. screenshots: 

Are you affected?
Enter the version of the package you're using.