GHSA-cmh9-rx85-xj38
XSS sidekiq-unique-jobs UI server vulnerability
Quick fix
GHSA-cmh9-rx85-xj38 — sidekiq-unique-jobs: upgrade to the fixed version with the command below.
bundle update sidekiq-unique-jobsDetails
### Summary
Cross site scripting (XSS) potentially exposing cookies / sessions / localStorage, fixed by `sidekiq-unique-jobs` v8.0.7.
Specifically, this is a Reflected (Server-Side), Non-Self, Cross Site Scripting vulnerability, considered a **_P3_** on the BugCrowd [taxonomy](https://bugcrowd.com/vulnerability-rating-taxonomy) with the following categorization: Cross-Site Scripting (XSS) > Reflected > Non-Self
It was initially thought there was a second vulnerability (RCE), but it was a false alarm. Injection is impossible with Redis:
> String escaping and NoSQL injection > The Redis protocol has no concept of string escaping, so injection is impossible under normal circumstances using a normal client library. The protocol uses prefixed-length strings and is completely binary safe.
Ref: https://redis.io/docs/management/security/
**XSS Vulnerability**
Specially crafted `GET` request parameters handled by any of the following endpoints of `sidekiq-unique-jobs`' "admin" web UI, allow a super-user attacker, or an unwitting, but authorized, victim, who has received a disguised / crafted link, to successfully execute malicious code, which could potentially steal cookies, session data, or local storage data from the app the `sidekiq-unique-jobs` web UI is mounted in.
1. `/changelogs` 2. `/locks` 3. `/expiring_locks`
This means if your `sidekiq-unique-jobs` web UI is mounted at `/sidekiq`, the vulnerable paths are:
1. `/sidekiq/changelogs` 2. `/sidekiq/locks` 3. `/sidekiq/expiring_locks`
XSS vulnerability is an instance of [CAPEC-32: XSS Through HTTP Query Strings](https://capec.mitre.org/data/definitions/32.html), which is related to [CWE-80](https://cwe.mitre.org/data/definitions/80.html). In certain cases where it results in a server error with status 500, it could be considered a vector for uncontrolled resource consumption, given that errors can be much more resource intensive that normal requests, and thus [CWE-400](https://cwe.mitre.org/data/definitions/400.html) & [CWE-754](https://cwe.mitre.org/data/definitions/754.html) may also be relevant.
### Details
Fix for the XSS vulnerability was released in `sidekiq-unique-jobs` [v8.0.7](https://github.com/mhenrixon/sidekiq-unique-jobs/releases/tag/v8.0.7).
This is an analogous attack vector to that which affected `sidekiq` gem from version v7.0.4 to v7.0.7, and was given identifiers [GHSA-h3r8-h5qw-4r35](https://github.com/advisories/GHSA-h3r8-h5qw-4r35) & [CVE-2023-1892](https://github.com/advisories/GHSA-h3r8-h5qw-4r35).
The vulnerability in `sidekiq-unique-jobs`' was *not* fixed by `sidekiq` [v7.0.8](https://github.com/sidekiq/sidekiq/blob/main/Changes.md#708), nor the more recent `sidekiq` [v7.2.0](https://github.com/sidekiq/sidekiq/blob/main/Changes.md#720) releases; they are similar but unrelated, distinct vulnerabilities in adjacent projects.
Note #1: The admin web UI for `sidekiq-unique-jobs` is not protected by any authorization constraint in the default configuration. Auth constraints must be configured by the programmer. It is recommended and expected that users will configure authorization constrains on the "admin" UI. This is not specifically related to the vulnerability but may make users who fail to constrain their "admin" UI even more vulnerable.
Note #2: Most users of the library will not have configured the UI on a sandboxed subdomain, making all their cookies, localStorage data and session secrets [vulnerable to exposure](https://liveoverflow.com/do-not-use-alert-1-in-xss/). The purpose of a sandboxed subdomain is expressly to prevent leaking sensitive data through XSS attacks.
XSS Fix PR: https://github.com/mhenrixon/sidekiq-unique-jobs/pull/829
### PoC
**XSS**
Use a string like: ``` %22%3E%3Cimg/src/onerror=alert(document.domain)%3E ``` as the value for one of the parameters that are handled without escaping. Reference: https://liveoverflow.com/do-not-use-alert-1-in-xss/
1. Visit [/sidekiq/changelogs](http://localhost:3000/sidekiq/changelogs) - with a crafted query string like one of the following: a. Screenshot: 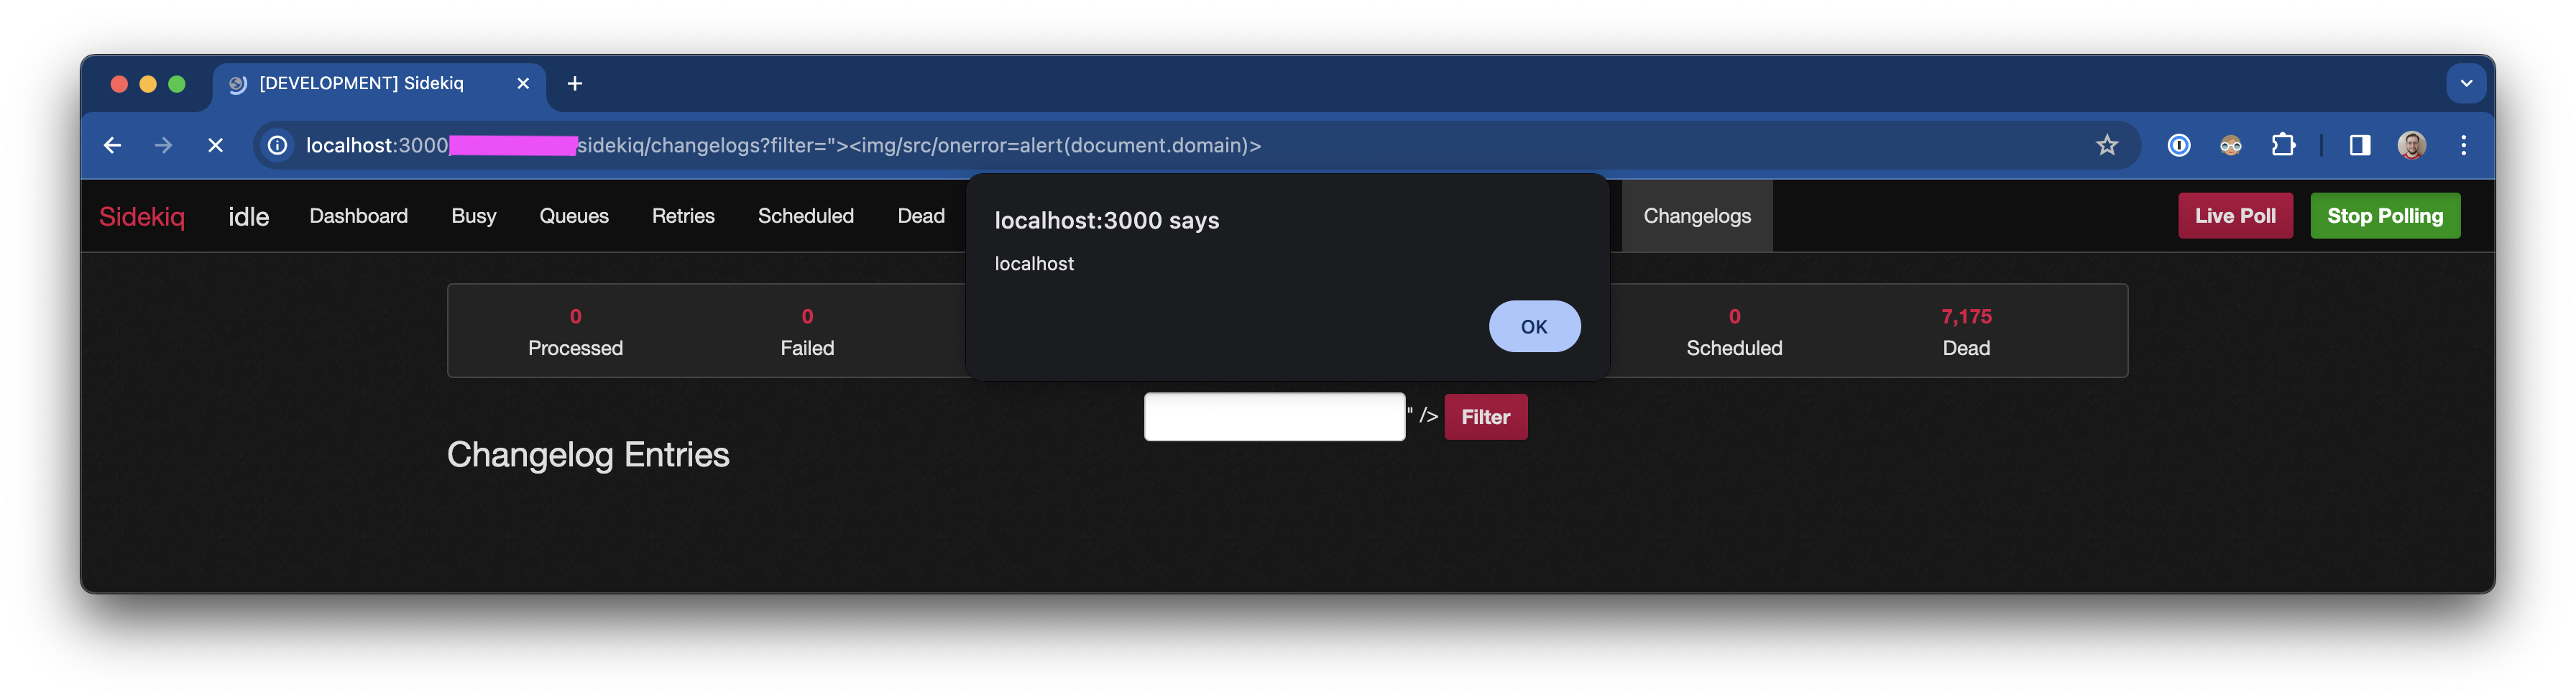 b. `filter` is XSS vulnerable: `?filter=%22%3E%3Cimg/src/onerror=alert(document.domain)%3E` c. `count` is vulnerable to triggering an application error (status 500), potentially allowing resource exhaustion `?count=%22%3E%3Cimg/src/onerror=alert(document.domain)%3E` 1. Screenshot: 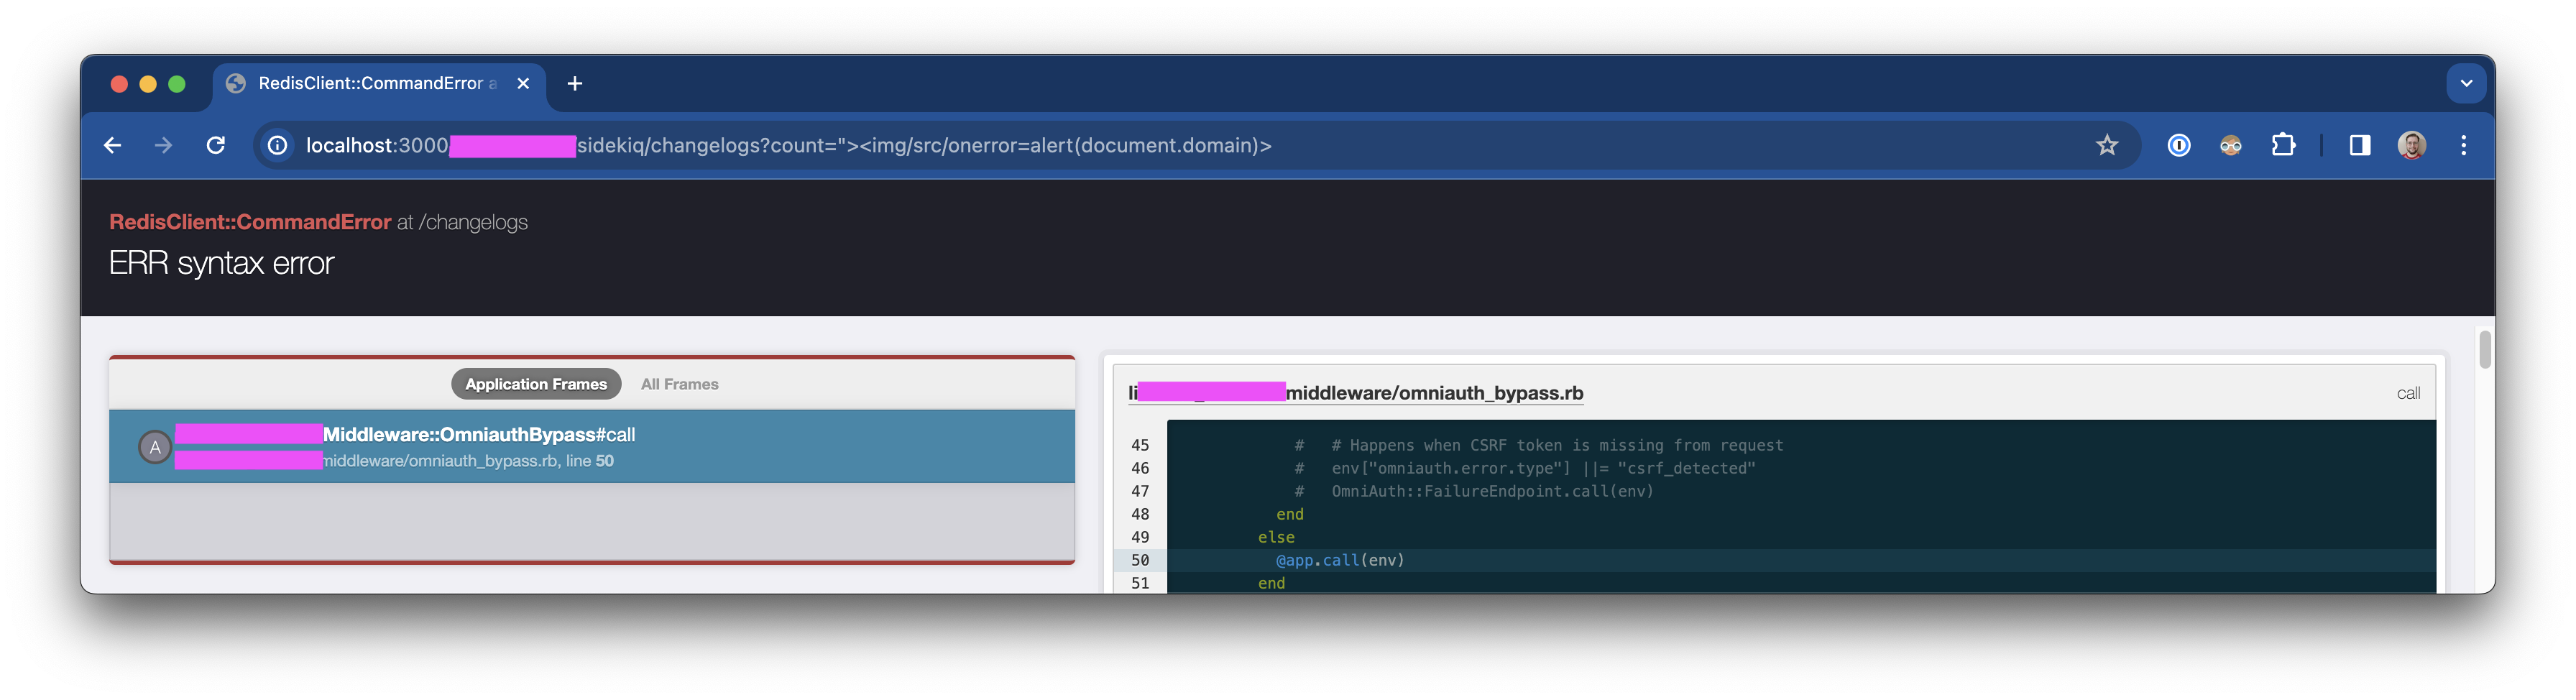 2. Visit [/sidekiq/locks](http://localhost:3000/sidekiq/locks) - with a crafted query string like one of the following: a. Screenshot: 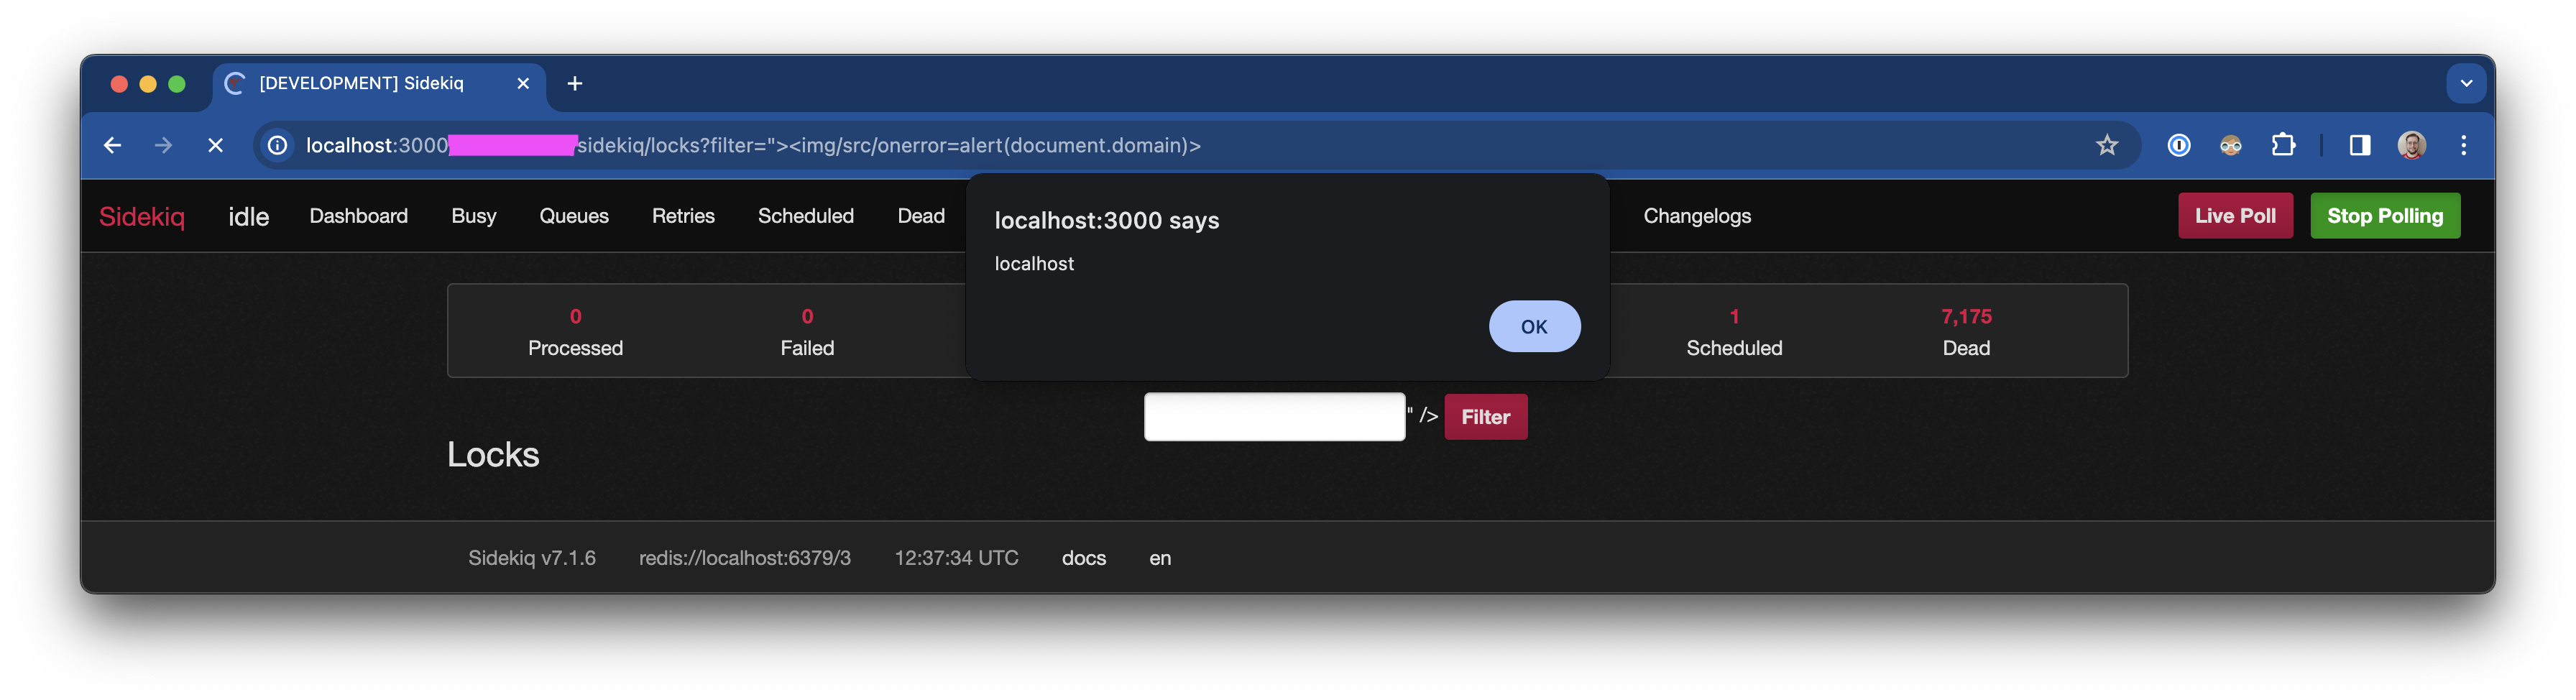 b. `filter` is XSS vulnerable: `?filter=%22%3E%3Cimg/src/onerror=alert(document.domain)%3E` c. `count` is vulnerable to triggering an application error (status 500), potentially allowing resource exhaustion `?count=%22%3E%3Cimg/src/onerror=alert(document.domain)%3E` 1. Screenshot: 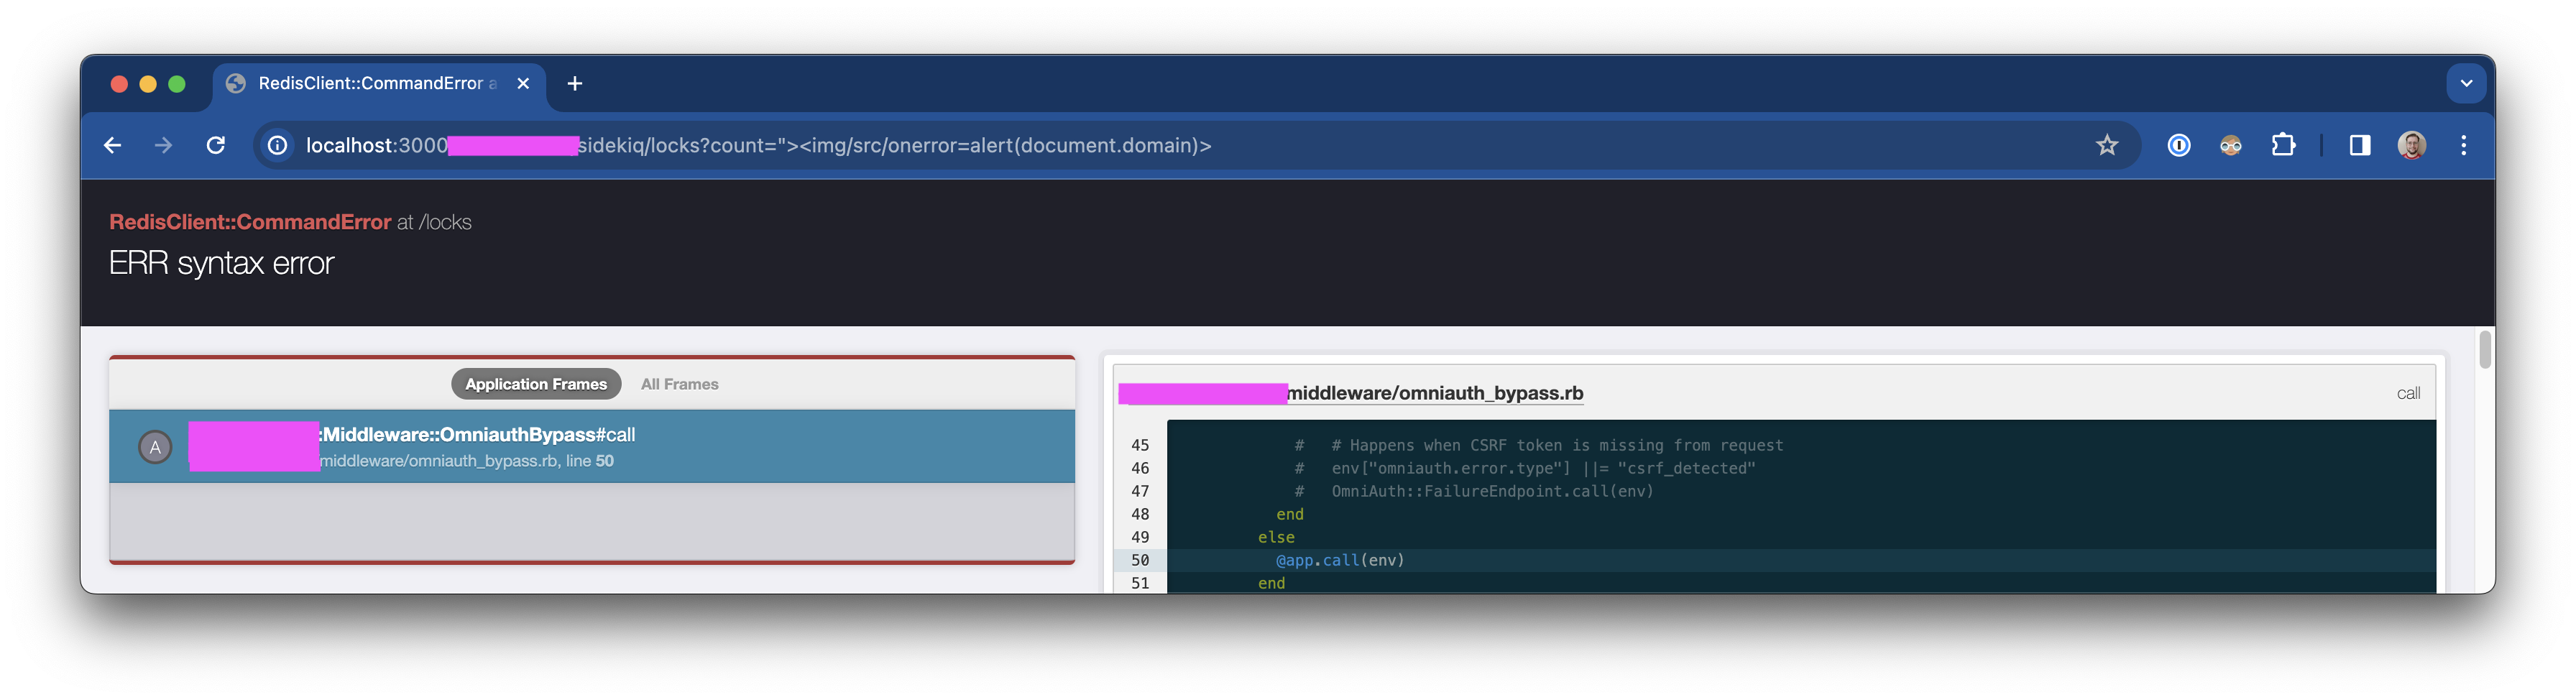 3. Visit [/sidekiq/expiring_locks](http://localhost:3000/sidekiq/expiring_locks) - with a crafted query string like one of the following: a. Screenshot: 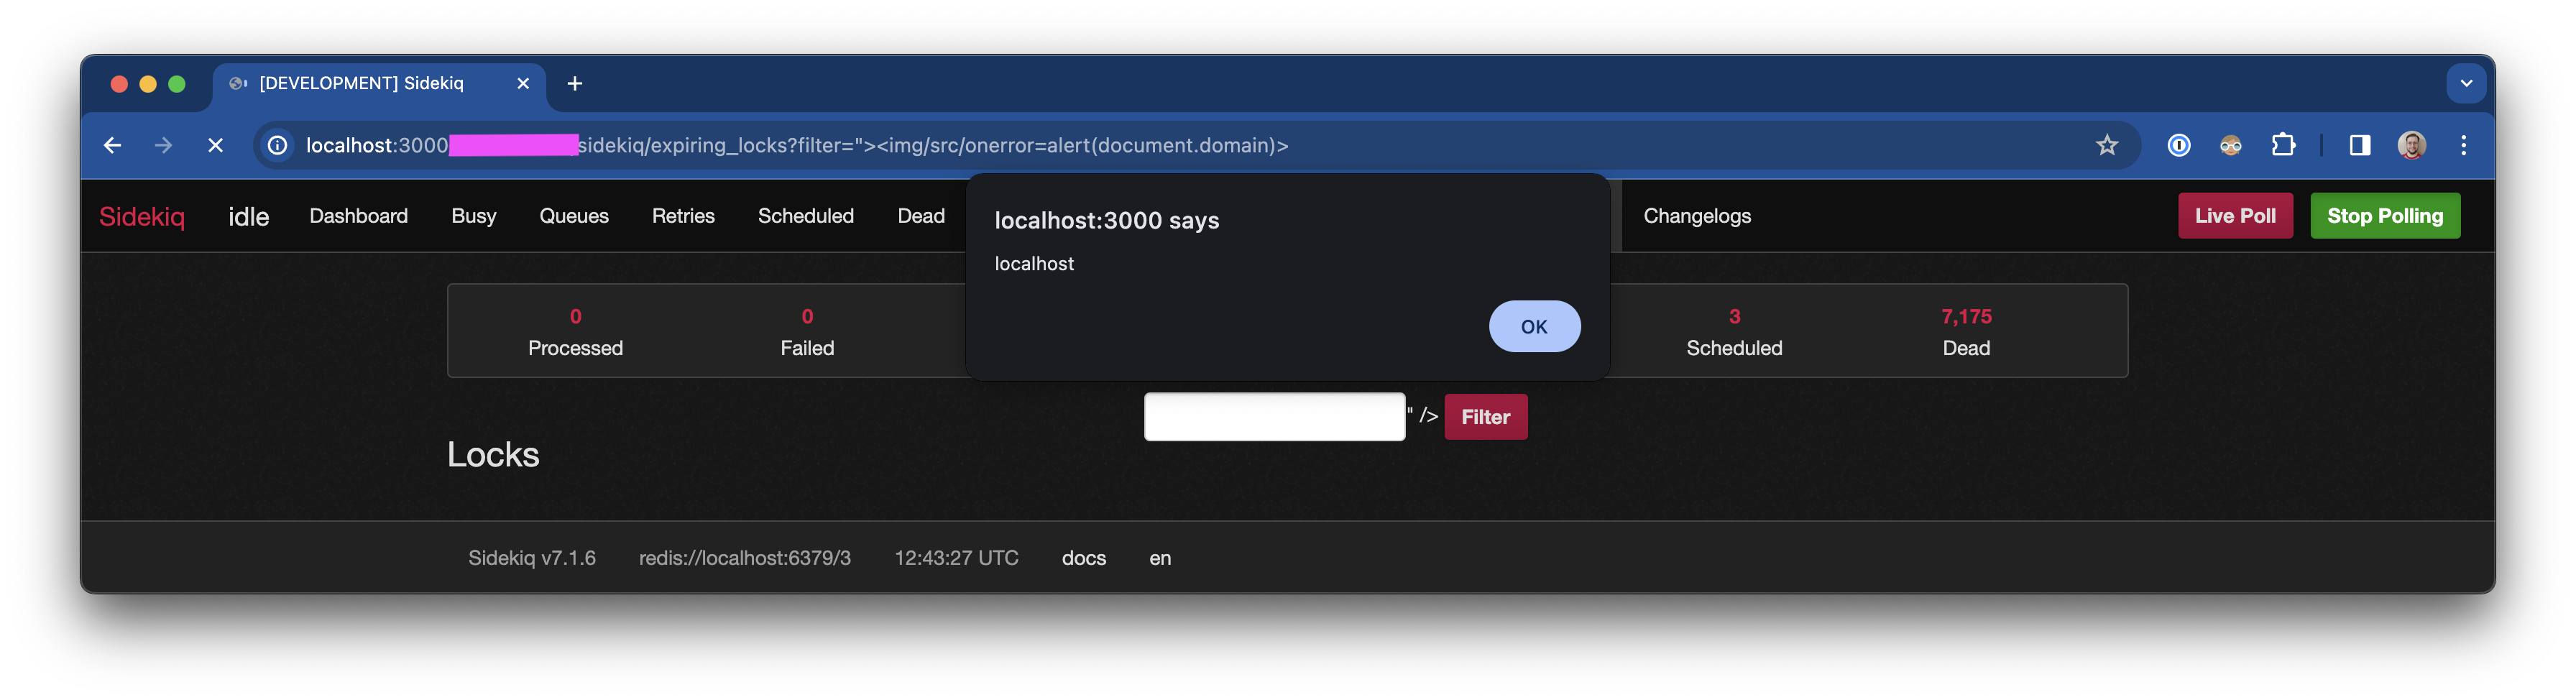 b. `filter` is XSS vulnerable: `?filter=%22%3E%3Cimg/src/onerror=alert(document.domain)%3E`
### Impact
This is a vulnerability of critical severity, which impacts many thousands of sites, since `sidekiq-unique-jobs` is widely deployed across the industry, with multiple attack vectors.
Are you affected?
Enter the version of the package you're using.
Affected packages
6.0.0.rc7Fixed in: 7.1.33bundle update sidekiq-unique-jobsReferences
- https://github.com/mhenrixon/sidekiq-unique-jobs/security/advisories/GHSA-cmh9-rx85-xj38[WEB]
- https://nvd.nist.gov/vuln/detail/CVE-2024-25122[ADVISORY]
- https://github.com/mhenrixon/sidekiq-unique-jobs/commit/cd09ba6108f98973b6649a6149790c3d4502b4cc[WEB]
- https://github.com/mhenrixon/sidekiq-unique-jobs/commit/ec3afd920c1b55843c72f748a87baac7f8be82ed[WEB]
- https://github.com/mhenrixon/sidekiq-unique-jobs[PACKAGE]
- https://github.com/rubysec/ruby-advisory-db/blob/master/gems/sidekiq-unique-jobs/CVE-2024-25122.yml[WEB]