GHSA-cwx6-cx7x-4q34
LibreNMS vulnerable to SQL injection time-based leads to database extraction
Quick fix
GHSA-cwx6-cx7x-4q34 — librenms/librenms: upgrade to the fixed version with the command below.
composer require librenms/librenms:^24.4.0Details
### Summary SQL injection vulnerability in POST /search/search=packages in LibreNMS 24.3.0 allows a user with global read privileges to execute SQL commands via the package parameter.
### Details There is a lack of hygiene of data coming from the user in line 83 of the file librenms/includes/html/pages/search/packages.inc.php 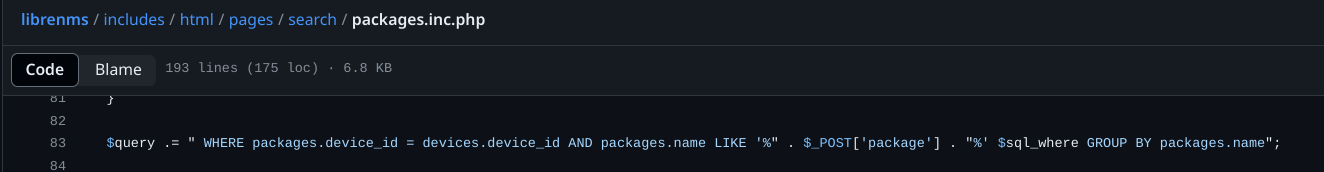
### PoC https://doc.clickup.com/9013166444/p/h/8ckm0bc-53/16811991bb5fff6
### Impact With this vulnerability, we can exploit a SQL injection time based vulnerability to extract all data from the database, such as administrator credentials
Are you affected?
Enter the version of the package you're using.
Affected packages
0Fixed in: 24.4.0composer require librenms/librenms:^24.4.0References
- https://github.com/librenms/librenms/security/advisories/GHSA-cwx6-cx7x-4q34[WEB]
- https://nvd.nist.gov/vuln/detail/CVE-2024-32461[ADVISORY]
- https://github.com/librenms/librenms/commit/d29201fce134347f891102699fbde7070debee33[WEB]
- https://doc.clickup.com/9013166444/p/h/8ckm0bc-53/16811991bb5fff6[WEB]
- https://github.com/librenms/librenms[PACKAGE]