GHSA-6p68-36m6-392r
phpMyFAQ Stored Cross-site Scripting at FAQ News Content
Quick fix
GHSA-6p68-36m6-392r — phpmyfaq/phpmyfaq: upgrade to the fixed version with the command below.
composer require phpmyfaq/phpmyfaq:^3.2.6Details
### Summary By manipulating the news parameter in a POST request, an attacker can inject malicious JavaScript code. Upon browsing to the compromised news page, the XSS payload triggers.
### PoC 1. Edit a FAQ news, intercept the request and modify the `news` parameter in the POST body with the following payload: `%3cscript%3ealert('xssContent')%3c%2fscript%3e` 2. Browse to the particular news page and the XSS should pop up. 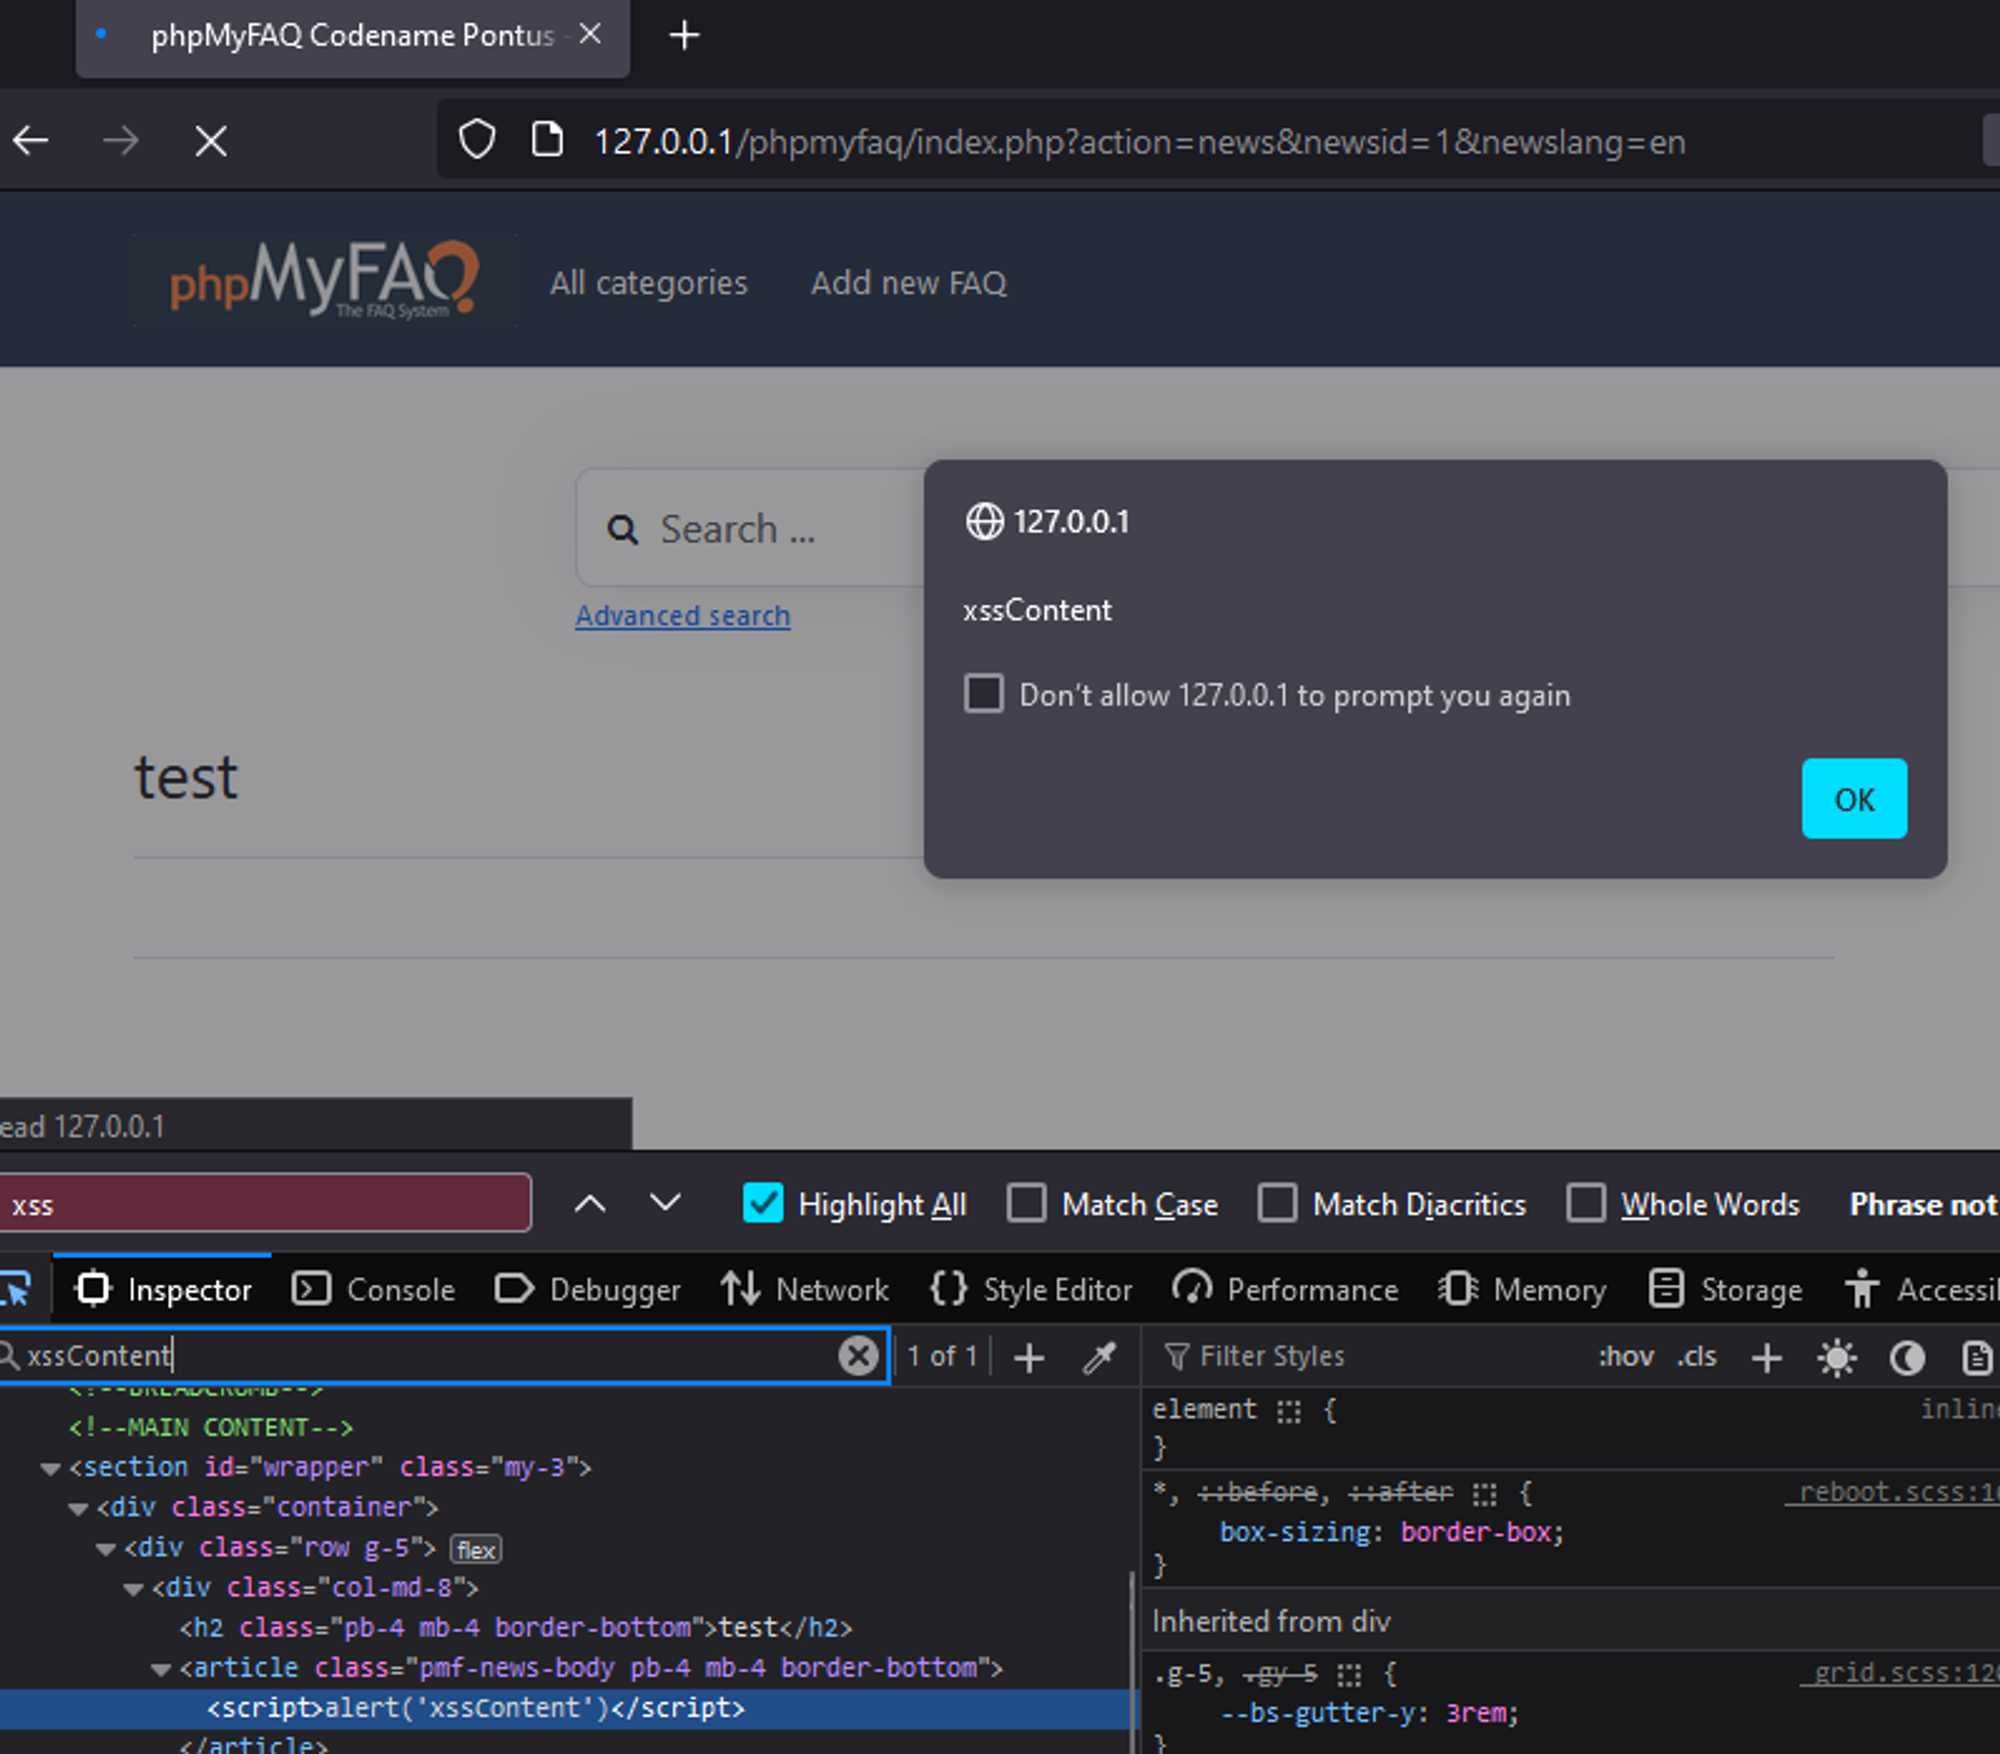
### Impact This allows an attacker to execute arbitrary client side JavaScript within the context of another user's phpMyFAQ session
Are you affected?
Enter the version of the package you're using.
Affected packages
3.2.5Fixed in: 3.2.6composer require phpmyfaq/phpmyfaq:^3.2.6